

Network-Security-Essentials PDF Dumps Jul 07, 2025 Exam Questions – Valid Network-Security-Essentials Dumps
Ultimate Network-Security-Essentials Guide to Prepare Free Latest WatchGuard Practice Tests Dumps
NEW QUESTION # 12
You configured your Firebox interfaces and routes and want to verify the status of the routes and connected hosts. You found this information in Firebox System Manager > Status Report. What is true about the IPv4 routes and ARP table in this deployment? (Select one.)
- A. The Firebox cannot resolve a MAC address for 10.0.1.32
- B. 10.0.20.53 can be reached through the vlan20 interface
- C. The Firebox is publicly reachable at 198.51.100.1 through the eth0 interface
- D. The MAC address for the default gateway that currently routes traffic is 00:50:56:b5:e5:42
- E. The MAC address for 172.16.1.20 is 00:50:56:b0:22:0f
Answer: C
Explanation:
Analyzing the routing table and ARP table in the provided image:
* Routing Table Analysis:
* The route 0.0.0.0 with a gateway of 198.51.100.1 on the eth0 interface suggests this is the default route for outbound traffic, indicating that the Firebox's public interface (eth0) is configured to route traffic through this gateway.
* This confirms that the Firebox is publicly reachable at the IP address 198.51.100.1.
* ARP Table Analysis:
* The ARP entry for the gateway IP 198.51.100.1 is not directly shown in the image but could typically be resolved to verify connectivity.
* Other options provided, such as MAC address validation, do not correspond with the current ARP entries shown in the image.
This setup indicates that the Firebox is accessible publicly on the eth0 interface using the IP 198.51.100.1, makingOption Athe correct answer.
NEW QUESTION # 13
There is an Internet outage at your primary ISP, but the Internet connection from the Firebox has not failed over to your backup ISP. Both ISP connectors are correctly cabled and have active physical links. What could cause this problem? (Select two.)
- A. The secondary IP addresses are not defined for the backup ISP interface
- B. Link Monitor target for the backup ISP interface is not responding
- C. The Link Monitor target for the primary ISP interface is set to ping the default gateway, but the outage is further upstream
- D. In the Multi-WAN settings, the Gradual Fallback option is enabled
- E. In the Multi-WAN settings, the Immediate Fallback option is enabled
Answer: B,C
Explanation:
* Link Monitor Target for Backup ISP: If the backup ISP's Link Monitor target is not responsive, the Firebox will not initiate a failover, as it interprets the backup connection as inactive or faulty.
* Primary ISP Link Monitor Configuration: When the Link Monitor for the primary ISP only checks the default gateway, it may not detect issues occurring further upstream. If the outage is beyond the gateway, failover will not activate because the monitor assumes the link is still valid.
These settings are critical to ensuring proper Multi-WAN failover behavior in case of ISP issues.
NEW QUESTION # 14
What does a Firebox configured with default firewall policies do with outbound traffic that does not have a configured route? (Select one.)
- A. Drops the traffic
- B. Denies the traffic
- C. Sends the traffic to the loopback interface
- D. Sends the traffic to the default gateway
Answer: A
Explanation:
When a Firebox is configured with default firewall policies and encounters outbound traffic that lacks a specified route, the Firebox will drop this traffic. In firewall configurations, if there's no matching route or policy, the traffic typically gets discarded by default to prevent unintended data leakage or unauthorized connections. This behavior is standard for most firewall devices to ensure secure handling of unconfigured paths.
NEW QUESTION # 15
You have five public IP addresses available from your ISP. When you create a Static NAT action, you want to specify one of the public IP addresses for inbound traffic but do not see it in the IP address drop-down list.
How can you change the Firebox configuration to see additional public IP addresses in the Static NAT action?
(Select one.)
- A. Configure 1-to-1 NAT for your entire subnet
- B. Add the IP addresses to the Dynamic NAT configuration
- C. Add secondary IP addresses to the external interface
- D. Enable the Set Source IP option in the policy
- E. Add the public IP addresses to the From field of the policy that uses the Static NAT action
Answer: C
Explanation:
To use additional public IP addresses in a Static NAT action, you need to add them as secondary IP addresses to the external interface on the Firebox. By adding these IPs as secondary addresses, they become selectable options in the Static NAT configuration, allowing inbound traffic to be routed based on specific public IPs allocated by the ISP.
NEW QUESTION # 16
Before packets are examined by Default Threat Protection, they are processed by firewall policies in top- down order.
- A. False
- B. True
Answer: B
Explanation:
In Firebox configuration, packets are processed by firewall policies in atop-down orderbefore they reach Default Threat Protection. This ordering ensures that the firewall policies defined higher in the policy list take precedence. Packets are evaluated against each rule sequentially from top to bottom until a matching policy is found, which then determines the action taken (allow, deny, or inspect further). Only after this process will any unfiltered traffic be subject to Default Threat Protection for additional security checks.
NEW QUESTION # 17
You bought a new Firebox and want to use the configuration from an existing Firebox you already configured. The best way to migrate the configuration is to restore a backup image from the existing Firebox to the new Firebox, then add the new feature key.
- A. False
- B. True
Answer: B
Explanation:
When migrating configurations from one Firebox to another, restoring a backup image from the existing Firebox to the new one is a valid and efficient method. This approach will transfer all configuration settings, policies, and security settings to the new Firebox. After restoring the backup, you need to add the new feature key specific to the new Firebox, as feature keys are unique to each device. This method preserves the existing configurations while adapting the setup for the new hardware.
NEW QUESTION # 18
You want to create a branch office VPN virtual interface between a remote Firebox and your headquarters Firebox so the remote Firebox can send log data to a server at headquarters. For the log data to be sent from the remote Firebox over the VPN successfully, what BOVPN virtual interface setting must you configure?
(Select one.)
- A. Virtual IP addresses
- B. Dead Peer Detection (DPD)
- C. IKEv2 in the Phase 1 settings
- D. Perfect Forward Secrecy (PFS)
- E. An IPSec certificate, instead of a Pre-shared key
Answer: A
Explanation:
To enable the remote Firebox to send log data to a server at headquarters through a Branch Office VPN (BOVPN) virtual interface, you must configureVirtual IP addresses. Virtual IPs enable devices on either end of the VPN tunnel to communicate as if they are on the same network, facilitating routing of log data from the remote Firebox to the log server located at headquarters.
Other options likeIPSec certificatesandIKEv2are not specifically required for this configuration, though they can enhance security.Dead Peer Detection (DPD)andPerfect Forward Secrecy (PFS)are useful for maintaining VPN stability and security but are not directly necessary for enabling log transmission.
NEW QUESTION # 19
In a Mobile VPN configuration, why would you choose default-route (full tunnel) VPN instead of split tunnel VPN? (Select one.)
- A. Default-route VPN is the only option you can use to apply security services to connections routed to your internal servers.
- B. Default-route VPN automatically allows dynamic NAT.
- C. Default-route VPN uses less processing power.
- D. Default-route VPN enables your Firebox to examine all remote user traffic.
- E. Default-route VPN uses less bandwidth.
Answer: D
Explanation:
In a Mobile VPN setup, adefault-route (full tunnel)VPN routes all of a remote user's internet traffic through the VPN tunnel to the Firebox. This configuration allows the Firebox to inspect and apply security policies to all traffic, including traffic that is not destined for internal network resources. In contrast, asplit tunnel VPN would route only traffic meant for the internal network through the VPN, while internet-bound traffic would bypass the Firebox, potentially exposing it to threats and limiting the Firebox's ability to inspect all traffic.
NEW QUESTION # 20
You lost access to a Firebox because no one knows the administrator passphrase. How can you regain access to the Firebox? (Select one.)
- A. Connect with a console cable to reset the passphrase
- B. Plug in a USB flash drive with the WatchGuard Password Reset utility loaded
- C. Reset the Firebox to its factory defaults
- D. Call WatchGuard Support for a passphrase reset
- E. Restore a backup image of the Firebox
Answer: C
Explanation:
If the administrator passphrase is lost:
* Option A: Resetting the Firebox to factory defaults is the recommended solution to regain access, as it clears the current configurations, including the admin passphrase, allowing reconfiguration from scratch.
* Option B(USB reset utility) andOption E(console cable reset) are not standard options for passphrase recovery on Firebox.
* Option C(Calling WatchGuard Support) cannot directly reset the passphrase.
* Option D(Restoring a backup) requires access to the device with the current passphrase.
NEW QUESTION # 21
When you migrate a configuration file from one Firebox to a new Firebox, which settings transfer to the new device? (Select two.)
- A. Management users
- B. Feature key
- C. Policies
- D. Certificates
- E. DNS servers
Answer: A,C
Explanation:
When migrating configurations:
* Option A: Management user settings transfer, preserving administrator access control configurations on the new device.
* Option C: Policies, including firewall rules, transfer, ensuring that network traffic handling settings are retained.
* Option B(Certificates) andOption D(DNS servers) are specific configurations often set manually and do not automatically transfer.
* Option E(Feature key) is unique to each device and must be installed separately on the new Firebox.
NEW QUESTION # 22
If policies are automatically ordered, which of these policies has the highest precedence? (Select one.)
- A. Outgoing policy - From: Any-Trusted, Any-Optional To: Any-External
- B. HTTPS policy - From: Any-Trusted, Any-Optional To: Any-External
- C. HTTPS policy - From: Trusted To: Any-External
- D. HTTPS policy - From: User1@Firebox-DB To: Any-External
Answer: D
Explanation:
When policies are automatically ordered, policies with more specific user-based criteria have higher precedence over general policies. In this scenario, an HTTPS policy for a specific user (e.g.,User1@Firebox- DB) would take precedence over policies that apply to broader groups or networks, such asAny-Trustedor Any-Optional. This ordering ensures that individual user rules are evaluated first before generic policies, providing finer access control.
NEW QUESTION # 23
Which of these sites are denied by the WebBlocker action shown in this image? (Select three.)
- A. login.facebook.com
- B. www.youtube.com
- C. schedule.myschool.edu
- D. www.wikipedia.com/firewall
- E. www.google.com
- F. www.watchguard.com/wgrd-blog
Answer: A,B,E
Explanation:
The WebBlocker action in the image contains bothAllowandDenyrules based on specific patterns:
* www.youtube.com- This is explicitly denied by the WebBlocker configuration for the pattern youtube.
com*.
* login.facebook.com- This would also be denied because it matches the pattern facebook.com*.
* www.google.com- There is no specificAllowrule for google.com or any associated subdomain, and since WebBlocker defaults toDenywhen a URL does not match any exceptions, www.google.com would be denied as well.
The other options:
* A.www.wikipedia.com/firewall- Allowed due to the wikipedia.com* pattern.
* D. schedule.myschool.edu- Allowed due to the regular expression matching *.myschool.edu.
* E.www.watchguard.com/wgrd-blog- Allowed by the regular expression for watchguard.com.
NEW QUESTION # 24
A Firebox backup image includes certificates that were previously imported to the Firebox.
- A. False
- B. True
Answer: B
Explanation:
A Firebox backup image indeed includes any certificates previously imported to the Firebox. This backup not only contains configurations and policies but also all associated certificates, ensuring that if a restoration is necessary, all security certificates will be restored alongside other settings. This feature is critical for maintaining the integrity and continuity of encrypted connections and secure communications across the Firebox environment.
NEW QUESTION # 25
Your users have no network connectivity on their computers in the 10.0.40.0/24 network. You investigate and discover the DHCP address pool for this network is exhausted, but there are no available IP addresses in the network to assign. Which of these options can you use to expand the IP address space of this network? (Select two.)
- A. Change the IP address of the 10.0.40.1/24 network to 10.0.40.123/24
- B. Add 10.0.50.1/24 to the 10.0.40.1/24 network as a secondary network
- C. Bridge the 10.0.40.1/24 network across additional interfaces
- D. Enable a wireless SSID for the 10.0.40.1/24 network
- E. Create a Dynamic NAT rule for traffic from the 10.0.40.1/24 network going to the 10.0.50.1/24 network
Answer: B,C
Explanation:
* Adding a Secondary Network (10.0.50.1/24): By adding a secondary subnet (such as10.0.50.1/24) to the existing 10.0.40.1/24 network, you expand the IP address space, effectively increasing the number of available IP addresses for DHCP allocation.
* Bridging Across Additional Interfaces: Bridging the 10.0.40.1/24 network across multiple interfaces can also increase the available address pool by creating a larger logical network. This approach helps manage IP space across a broader range of devices without subnet fragmentation.
These methods provide scalable solutions to expand IP address availability within constrained network spaces.
NEW QUESTION # 26
Match the "network server to the protocol and port it uses."
Answer:
Explanation: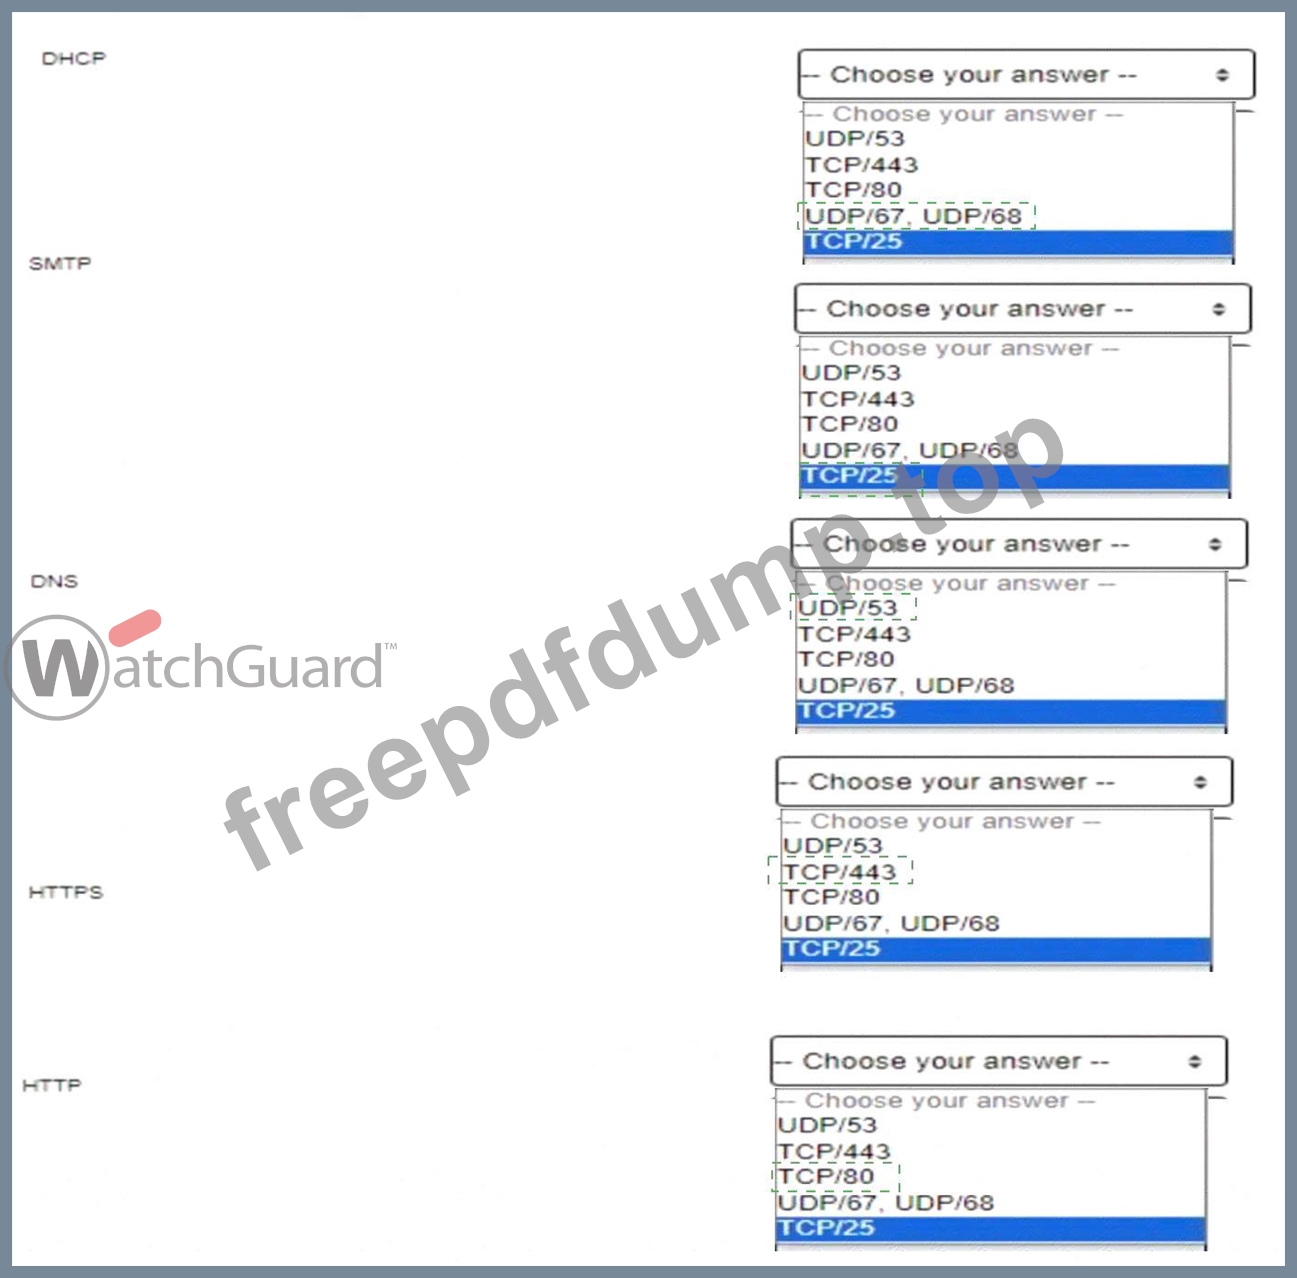
Explanation: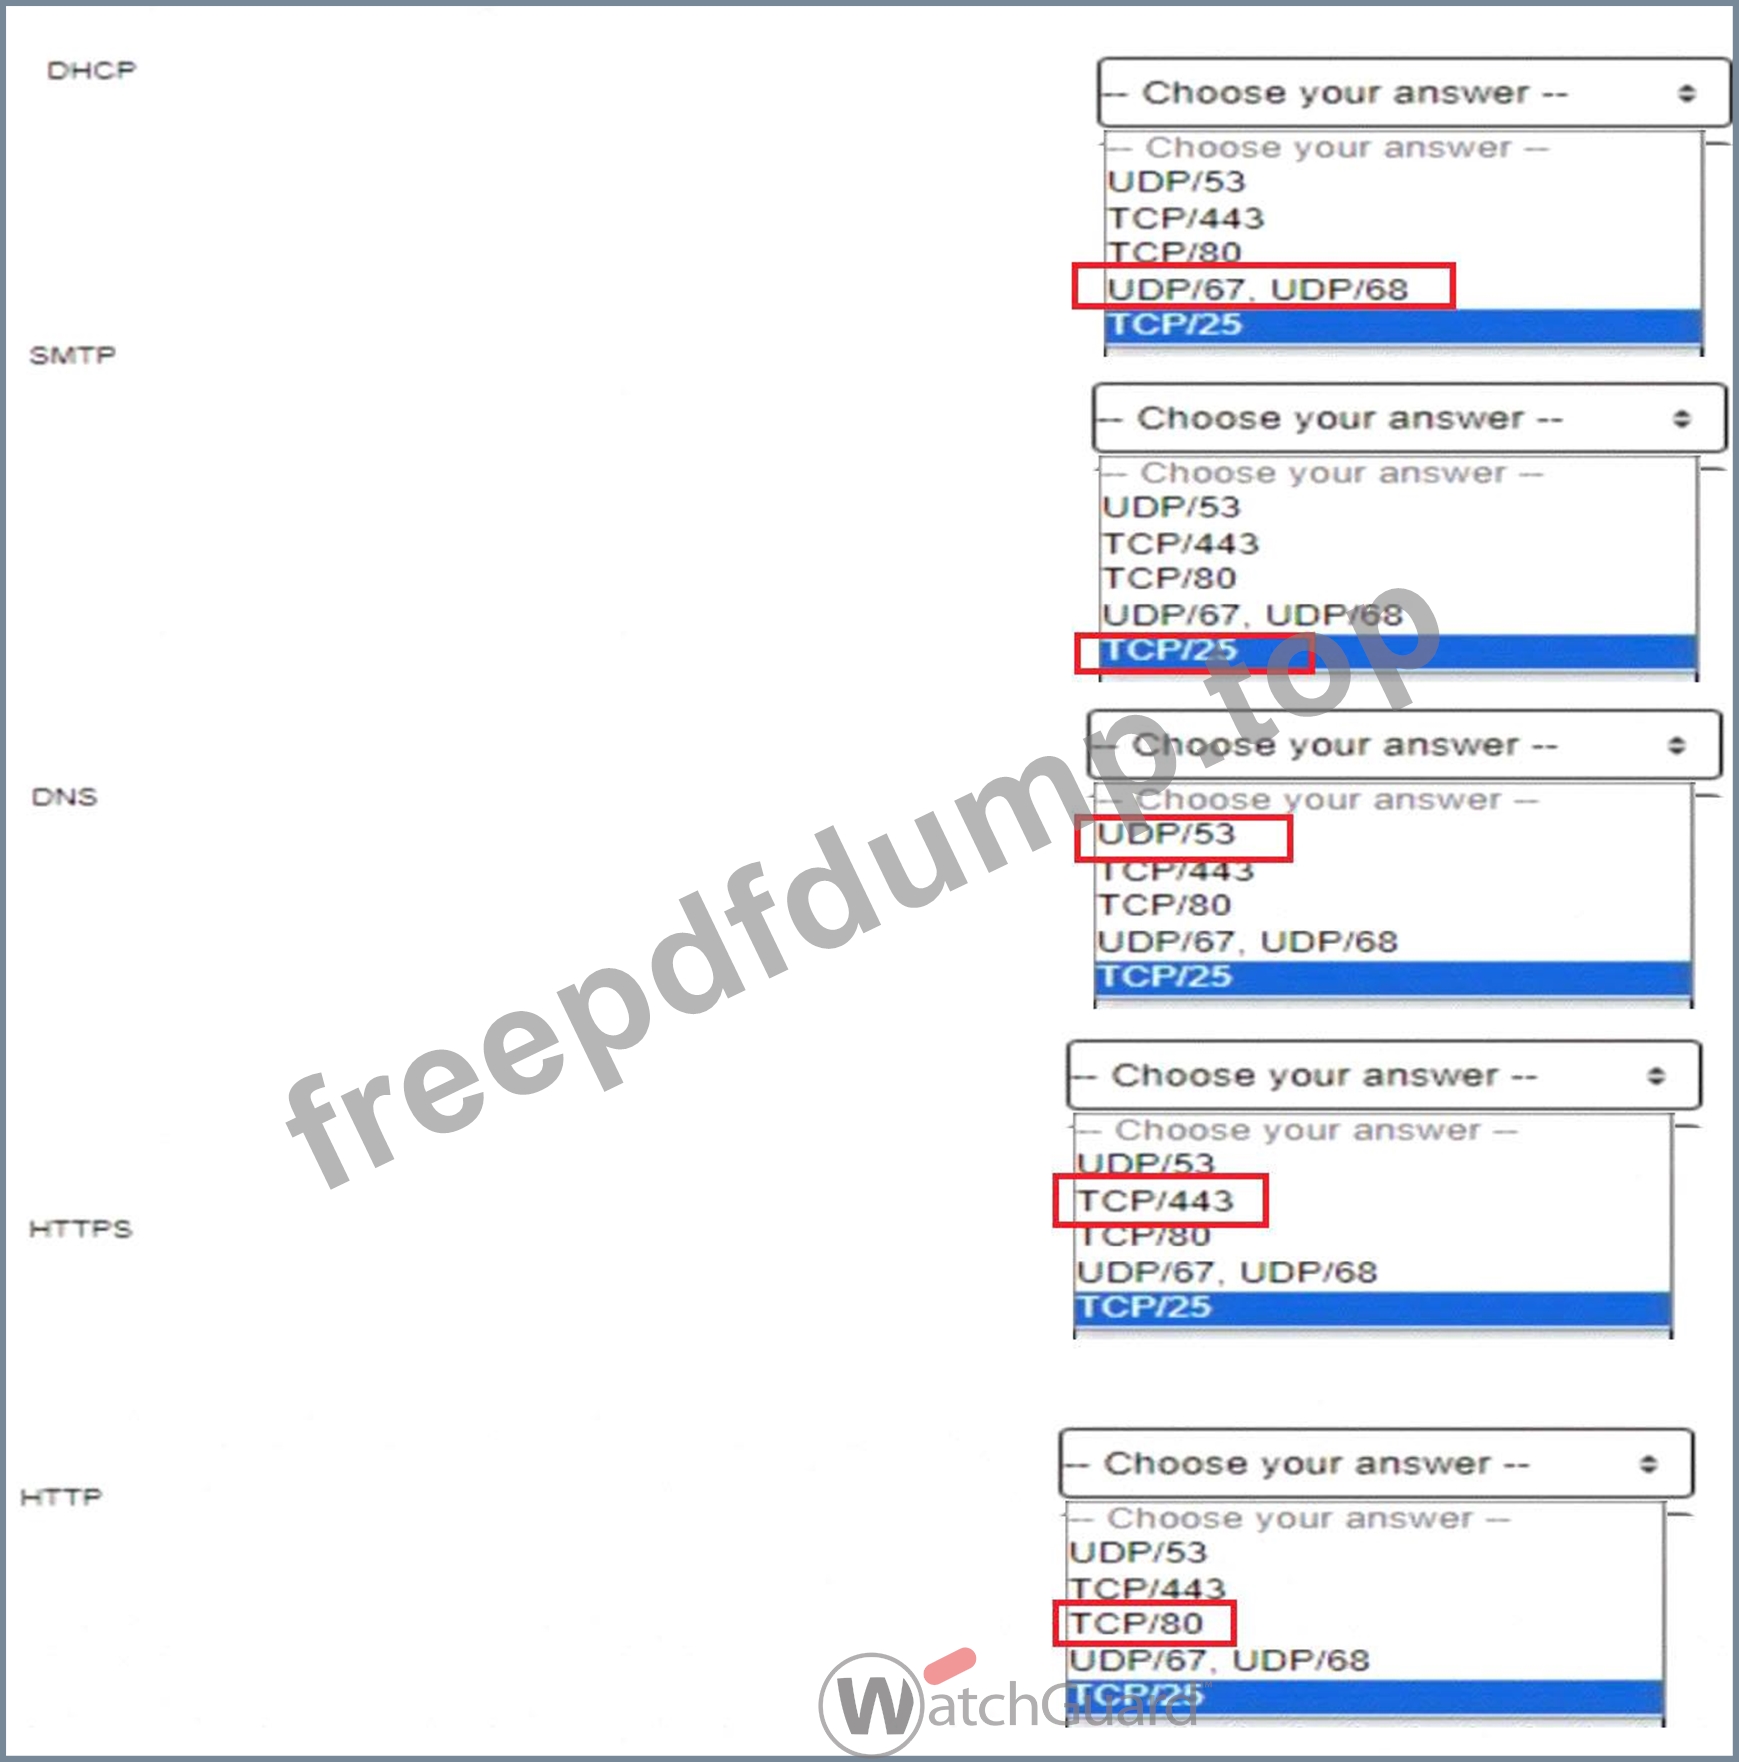
DHCP (Dynamic Host Configuration Protocol):DHCP operates over UDP ports 67 and 68. Port 67 is used by the DHCP server to listen for client requests, and port 68 is used by the DHCP client. This allows devices to automatically receive IP addresses and other network configuration details on a network, essential for automating IP management. [Referenced from multiple sources on network fundamentals] SMTP (Simple Mail Transfer Protocol):SMTP uses TCP port 25 for sending emails from client to server or between mail servers. SMTP is integral for email transmission, allowing efficient communication across mail servers within and outside organizational networks. [Referenced in standard protocols documentation in network management guides] DNS (Domain Name System):DNS typically runs on UDP port 53 for standard queries, with TCP/53 used for zone transfers and other larger requests. DNS is critical for resolving human-readable domain names into IP addresses, which allows users to connect to websites using easily remembered names rather than numerical IP addresses. [Foundational knowledge as detailed in network security and management resources] HTTPS (Hypertext Transfer Protocol Secure):HTTPS, an encrypted version of HTTP,operates on TCP port 443. It provides secure communication over the internet by encrypting data between the client and server using SSL/TLS, protecting data integrity and privacy. [Security essentials for network communications as found in secure web traffic documentation] HTTP (Hypertext Transfer Protocol):HTTP operates on TCP port 80 and is used for unencrypted web traffic. HTTP is the foundation of data exchange on the World Wide Web, supporting basic client-server interactions for retrieving resources from the web. [Basic networking knowledge referenced across multiple network essentials texts]
NEW QUESTION # 27
A Firebox has an external IP address of 203.0.113.100. A public web server with the IP address 10.0.1.80 is connected to a Firebox internal network. What is the effect of the policy shown in this image? (Select one.)
- A. Allows users on the Internet and the 10.0.1.0/24 network to use the external IP address of the Firebox to connect to the web server
- B. Applies dynamic NAT to the 10.0.1.80 IP address of the web server to allow inbound connections
- C. Allows users on the Internet to connect to the 10.0.1.80 IP address of the web server
- D. Allows users on the Internet and the 10.0.1.0/24 network to use the internal IP address of the Firebox to connect to the web server
Answer: A
Explanation:
In the policy configuration shown in the image:
* From Section: It specifies "Any-External" and 10.0.1.0/24, indicating that this policy applies to traffic from any external source (Internet users) as well as from devices on the internal network 10.0.1.0/24.
* To Section: The destination specifies a public-facing IP address (203.0.113.100) that is statically NAT'd to the internal IP address of the web server (10.0.1.80). This means external users and internal users can access the web server using the Firebox's external IP.
* Effect of Static NAT: The policy uses Static NAT to map the Firebox's external IP address to the web server's internal IP address, allowing inbound connections to reach the server. This setup provides consistent access for both external and internal users via the same public IP address.
This configuration effectively enables both Internet users and users within the specified internal network (10.0.1.0/24) to connect to the web server using the Firebox's external IP, makingOption Dthe correct answer.
NEW QUESTION # 28
Clients on the 10.0.10.0/24 network must connect to the server at 10.0.20.100. Based on this image, what static route must you add to the Firebox for traffic to reach the server? (Select one.)
- A. Route to 10.0.20.0/24, Gateway 10.0.2.1
- B. Route to 10.0.2.0/24, Gateway 10.0.2.1
- C. Route to 10.0.20.0/24, Gateway 10.0.2.254
- D. Route to 10.0.10.0/24, Gateway 10.0.0.1
- E. Route to 10.0.20.0/24, Gateway 10.0.2.254
Answer: E
Explanation:
In this network configuration:
* The Firebox needs a static route to direct traffic intended for the 10.0.20.0/24 network (where the server
10.0.20.100 resides).
* The gateway address that allows the Firebox to reach the 10.0.20.0/24 network is 10.0.2.254, which is the router's IP address on the 10.0.2.0/24 network.
By configuring a static route:
* Destination: 10.0.20.0/24
* Gateway: 10.0.2.254
This route instructs the Firebox to send traffic destined for the 10.0.20.0/24 network via the router at
10.0.2.254, enabling clients in the 10.0.10.0/24 network to reach the server.
* Option Bis correct because it provides the correct destination and gateway for traffic to the 10.0.20.0
/24 network.
* Option Aincorrectly sets the route to 10.0.10.0/24, which doesn't address the server network.
* Options C and Dset incorrect gateways (10.0.2.1), which do not route traffic correctly in this setup.
* Option Eis a duplicate of B and would also be correct; thus, B and E are equivalent.
NEW QUESTION # 29
You enable a network device monitoring application on a server with IP address 10.0.1.22. After you run the application, it reports that it cannot ping the Firebox at 10.0.1.1, and you see this log message in Traffic Monitor. What is the most likely cause of this issue? (Select one.)
- A. The dynamic NAT statement is not configured correctly for the 10.0.1.0/24 subnet
- B. There is no route on the Firebox for the 10.0.1.0/24 subnet
- C. There is no policy that allows Ping traffic from the server to the Firebox alias
- D. The server IP address is on the Blocked Sites list
- E. The default Unhandled Internal Packet policy is at the top of the policy set
Answer: C
Explanation:
The most likely reason for the network device monitoring application's failure to ping the Firebox is the absence of an explicit policy permitting Ping traffic from the server (IP 10.0.1.22) to the Firebox alias (10.0.1.1). By default, Firebox policies are configured to allow only traffic explicitly permitted by a policy.
Therefore, without a dedicated policy allowing ICMP (Ping) requests from this specific source to the Firebox, the device will drop the traffic, resulting in a connectivity failure for Ping.
This is a common scenario in Firebox configurations, where restrictive policy settings enhance network security by blocking all traffic types unless specifically allowed.
NEW QUESTION # 30
The Firebox can scan the contents of encrypted zip files with Gateway AntiVirus when HTTPS content inspection is enabled.
- A. True
- B. False
Answer: B
Explanation:
The Firebox cannot scan the contents of encrypted zip files even if HTTPS content inspection is enabled.
HTTPS content inspection allows the Firebox to inspect encrypted HTTPS traffic by decrypting it. However, the content within encrypted zip files remains inaccessible to Gateway AntiVirus scanning because the encryption key for the zip file is not available to the Firebox. This limitation is consistent with standard network security practices, where encrypted files need to be decrypted with a known key before content scanning can occur.
NEW QUESTION # 31
What are some advantages of BOVPN virtual interfaces (route-based VPN) over classic policy-based BOVPNs? (Select two.)
- A. More flexible routing options
- B. Additional encryption options
- C. Increased BOVPN throughput
- D. Supports VPN connectivity to cloud services
- E. Additional keep-alive options
Answer: A,D
Explanation:
BOVPN virtual interfaces (route-based VPNs)offer several advantages over traditional policy-based BOVPNs:
* Supports VPN connectivity to cloud services (A): Route-based VPNs can more easily integrate with cloud environments, as they use routing rather than specific policies, making it possible to route traffic to various cloud services and manage cloud-based VPN connections.
* More flexible routing options (C): Route-based VPNs allow administrators to define more granular routing rules using standard IP routing tables. This flexibility supports complex network architectures and multiple routes for redundancy or load balancing.
These features make route-based VPNs more adaptable to modern network needs, particularly in hybrid and multi-cloud environments.
NEW QUESTION # 32
You configured email notifications in WatchGuard Cloud for your Firebox Device Alarms and want to receive an email when your users download any .exe files through an HTTP proxy. You must enable what type of log message in the Firebox configuration? (Select one.)
- A. Alarm logs for when a virus is detected in the HTTP proxy
- B. Diagnostic logs for Gateway AntiVirus
- C. Denied traffic logs for the HTTP proxy policy
- D. Allowed traffic logs for the HTTP proxy policy
- E. Alarm logs for the EXE/DLL Body Content rule in the HTTP proxy
Answer: E
Explanation:
To receive email notifications when users download .exe files through an HTTP proxy, you need to enable Alarm logs for the EXE/DLL Body Content rulein the HTTP proxy configuration on the Firebox. This setting ensures that alerts are triggered whenever executable files are detected, and WatchGuard Cloud can send notifications based on these alarms.
Other logging options, such as allowed or denied traffic logs, would not provide the specific alerts required for .exe file downloads through the proxy.
NEW QUESTION # 33
As you troubleshoot a Branch Office VPN tunnel, you see the log message below. Which settings can you modify in the BOVPN virtual interface configuration to resolve this issue? (Select one.)
- A. Phase 1 Settings
- B. Phase 2 Settings
- C. VPN Routes
- D. Gateway Settings
- E. BOVPN-Allow policies
Answer: B
Explanation:
When troubleshooting a Branch Office VPN (BOVPN) tunnel, issues in thePhase 2 settingscan commonly cause connectivity problems. Adjusting settings such as the encryption and integrity algorithms, or setting correct lifetimes in Phase 2, may resolve compatibility or timeout issues with third-party VPN endpoints. This configuration ensures the two VPN endpoints can securely exchange data in alignment with each other's capabilities and settings.
NEW QUESTION # 34
After you enable content inspection, your users cannot connect to the business-critical website www.example.
com/account.html hosted by a trusted partner. To try to resolve this issue, you added a Domain Name exception of www.example.com/account.html, but users still cannot connect to the website. What is the Domain Name exception format to add to the HTTP proxy to correctly resolve this issue? (Select two.)
- A. /account.html
- B. /example.com/
- C. *.example.com
- D. example.com/
- E. www.example.com
Answer: C,E
Explanation:
When using domain exceptions to bypass content inspection for specific websites on a Firebox, the format is critical. For the domain www.example.com/account.html, two viable exception formats are:
* A. *.example.com: This wildcard format will include all subdomains of example.com, covering www.
example.com as well as any other subdomains like api.example.com. This format is useful when you need to exclude an entire domain and its subdomains from content inspection.
* D. www.example.com: This specifies the exact domain. Adding this as an exception will directly match www.example.com, making it suitable for bypassing content inspection on that specific subdomain.
Other formats, like /example.com/ or /account.html, do not match the required structure for domain name exceptions in the Firebox HTTP proxy settings.
NEW QUESTION # 35
If you have only one public IP address, can you use Static NAT to enable inbound connections to both an email server and a web server on the private network? (Select one.)
- A. Yes, if both servers use different ports
- B. Yes, if both servers are on different private subnets
- C. No, you must assign a public IP address to each server
- D. No, you must use Dynamic NAT to route inbound connections to more than one server
Answer: A
Explanation:
With only one public IP address, you can still configure Static NAT to route connections to both an email server and a web server, as long as each service is accessed on a different port. For instance, HTTP/HTTPS traffic for the web server can use port 80/443, while the email server can use ports associated with email protocols (e.g., 25 for SMTP). Static NAT can direct incoming requests to different internal servers based on port, making this approach feasible.
NEW QUESTION # 36
......
Passing Key To Getting Network-Security-Essentials Certified Exam Engine PDF: https://www.freepdfdump.top/Network-Security-Essentials-valid-torrent.html
Get Top-Rated WatchGuard Network-Security-Essentials Exam Dumps Now: https://drive.google.com/open?id=1ceaTghepUS6-hyCv1LqIoROE-FnxKom-
