

[Oct 27, 2024] Lesson Brilliant PDF for the NCP-CI-AWS Tests Free Updated Today
Get New 2024 Valid Practice Nutanix Certified Professional NCP-CI-AWS Q&A - Testing Engine
NEW QUESTION # 32
Which two statements are the most accurate regarding Cluster Protect? (Choose two.)
- A. Nutanix Guest Tools (NGT) is not required to be installed on User VMs.
- B. The Cluster Protect feature requires AOS version 6.7 or higher.
- C. The dusters that are to be protected must be registered with the same instance of Prism Central.
- D. An AWS subnet can be shared by VMs, Prism Central, and Multicloud Snapshort Technology (MST).
Answer: B,C
Explanation:
The clusters that are to be protected must be registered with the same instance of Prism Central (Answer C):
For Cluster Protect to function correctly, all clusters intended for protection must be registered under the same Prism Central instance. This ensures consistent management and coordination of protection policies and operations across clusters.
The Cluster Protect feature requires AOS version 6.7 or higher (Answer D):
Cluster Protect is a feature that is available starting from AOS version 6.7. To utilize this feature, ensure that the Nutanix clusters are running this version or a newer one.
Reference:
Nutanix Cluster Protection Documentation
Nutanix AOS Release Notes
NEW QUESTION # 33
An administrator seeks to ensure that the newly created NC2 organization named Finance can only deploy clusters into certain cloud regions.
What action should the administrator take to do this?
- A. Configure RBAC roles on the Finance NC2 organization to allow access to regions.
- B. Specify allowed regions when configuring a cloud account for the Finance NC2 organization.
- C. Configure IAM permission in cloud accounts to restrict access to certain regions.
- D. Open a support ticket with Nutanix to whitelist the allowed regions for the Finance NC2 organization.
Answer: B
Explanation:
To ensure that the newly created NC2 organization named Finance can only deploy clusters into certain cloud regions, the administrator should specify the allowed regions during the cloud account configuration.
This action restricts the regions available for cluster deployment, ensuring compliance with organizational policies or regulatory requirements.
The allowed regions can be set in the cloud account settings associated with the Finance NC2 organization, defining the geographical scope of operations.
Reference:
Refer to the Nutanix documentation on NC2 cloud account configuration and region restrictions.
NEW QUESTION # 34
Administrator has recently deployed an NC2 cluster on AWS in the North Virginia region in availability zone us-east-id. The consuming IPS from a 10.78.2.0/24 range.
The AWS VPC has two available CIDR ranges:
10.78.0.0/16
10.19.101.0/24
The following subnet have been configured in the NC2 AWS VPC: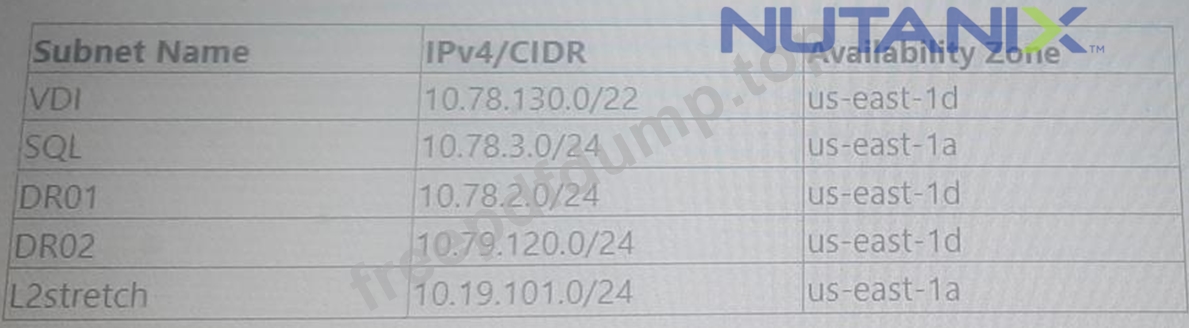
Which two subnet will show up in the Network configuration of the Prism Element Settings page? (Choose two.)
- A. VDI
- B. DR02
- C. L2stretch
- D. DR01
Answer: C,D
Explanation:
For the NC2 cluster deployed in the North Virginia region (us-east-id), consuming IPs from the 10.78.2.0/24 range, the subnets configured within the same CIDR range of 10.78.0.0/16 will be recognized.
The subnet DR01 (10.78.2.0/24) is directly within the range of the deployed cluster.
The subnet L2stretch (10.19.101.0/24) is also configured in the NC2 AWS VPC, although not in the immediate range of the cluster, it may show up due to broader network configurations for stretched L2 operations.
Subnets VDI (10.78.130.0/22) and DR02 (10.79.120.0/24), although part of the same VPC, are not directly within the immediate CIDR range or may not be recognized in this specific configuration scenario.
Reference:
Refer to the Nutanix documentation on NC2 AWS VPC subnet configurations and Prism Element settings for detailed guidelines on network visibility and configuration.
NEW QUESTION # 35
An administrator has recently deployed an NC2 on AWS cluster in the North Virginia region in availability zone us-east-1z. The clusters UUID is 0005F487-4962-91EA-4C98-C4284D123835.
The cluster is consuming IPs from a 10.78.2.0/24 range.
The AWS VPC has these available CIDR ranges:
* 70.73.0.0/16
* 10.79.107.0/24
* 10.0.0.0/22
The following subnets have been configured in the NC2 AWS VPC: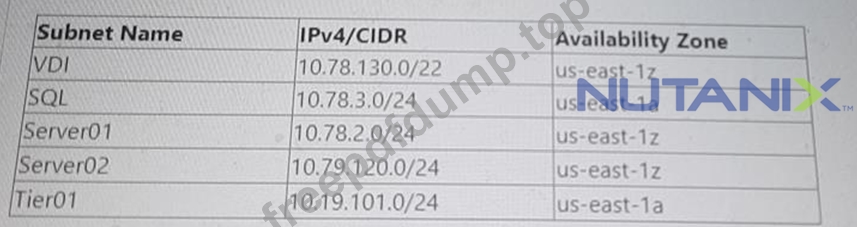
The following tags have been applied to a Custom Network Security Group: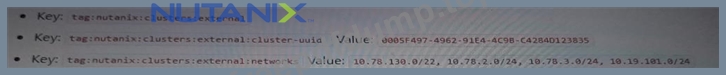
The Custom Network Security Group is allowing all inbound traffic from the 10.0.0.0/22 network. Which two subnets would be able to receive inbound traffic from AWS instances on a 10.0.0.0/22 network segment"? (Choose two.)
- A. Tier01
- B. Server01
- C. SQL
- D. VDl
Answer: A,B
Explanation:
To determine which subnets would be able to receive inbound traffic from AWS instances on a 10.0.0.0/22 network segment, we need to look at the configured subnets and their CIDR ranges, as well as the custom network security group's inbound rules.
Available CIDR ranges in VPC:
70.73.0.0/16
10.79.107.0/24
10.0.0.0/22
Configured Subnets in NC2 AWS VPC:
VDI: 10.78.130.0/22
SQL: 10.78.3.0/24
Server01: 10.78.2.0/24
Server02: 10.79.120.0/24
Tier01: 10.19.101.0/24
Custom Network Security Group Inbound Rule:
Allows all inbound traffic from 10.0.0.0/22.
Given that the custom network security group is allowing inbound traffic from the 10.0.0.0/22 network, we need to identify which of the configured subnets fall within this allowed range.
Analysis:
The subnets 10.78.130.0/22, 10.78.3.0/24, 10.78.2.0/24, 10.79.120.0/24, and 10.19.101.0/24 do not overlap with 10.0.0.0/22. Therefore, none of these subnets would naturally fall within the 10.0.0.0/22 range directly.
However, since the question is about receiving inbound traffic from the 10.0.0.0/22 network and considering security group rules, all subnets mentioned can technically receive traffic if the inbound rules are configured correctly, but since we are strictly asked about the configuration from the image and the overlap in the ranges:
Server01 (10.78.2.0/24) and Tier01 (10.19.101.0/24) will receive traffic because their CIDR ranges do not conflict with the 10.0.0.0/22 range, thus allowing traffic without additional restrictions.
Reference:
Nutanix Clusters on AWS Administration Guide
AWS VPC and Subnet documentation
Network Security Group rules configuration in Nutanix documentation
NEW QUESTION # 36
Which address must AWS Directory Service be able to resolve when deploying a new NC2 cluster?
- A. gateway-internal-api.cloud.nutanix.com
- B. gateway-external-api. cloud, nutanix.com
- C. dovvnloads.cloud.nutanix.com
- D. apikeys.nutanix.com
Answer: B
Explanation:
When deploying a new NC2 cluster, the AWS Directory Service must be able to resolve the address gateway-external-api.cloud.nutanix.com.
This external API gateway is critical for the NC2 cluster to communicate with Nutanix services for operations such as management, updates, and licensing.
Ensuring that this address can be resolved allows the cluster to interact properly with the Nutanix cloud infrastructure and services.
Reference:
Refer to the Nutanix documentation on network and DNS requirements for NC2 deployments, specifically the addresses that need to be resolvable for proper functionality.
NEW QUESTION # 37
In which two ways should an NC2 on AWS cluster be hibernated manually? (Choose two.)
- A. Select the cluster under NC2 console and Select Hibernate/Resume on the cluster sur page.
- B. Log into Prism, Central, navigate to Planning, find hibernate and resume.
- C. Log into Prism Element navigate to Settings and select Hibernate/Resume.
- D. Log into NC2 console, find the cluster name and select Hibernate/Resume from the ellipses.
Answer: A,D
Explanation:
To manually hibernate an NC2 on AWS cluster, the administrator can use the following methods:
Select the cluster under NC2 console and Select Hibernate/Resume on the cluster sur page: Navigate to the specific cluster in the NC2 console and use the provided Hibernate/Resume option.
Log into NC2 console, find the cluster name and select Hibernate/Resume from the ellipses: Access the NC2 console, locate the cluster name, and select the Hibernate/Resume option from the ellipses (three dots) menu.
These options allow for the manual control of the cluster's hibernation state directly within the NC2 console interface.
Reference:
Nutanix Cloud Clusters on AWS Administration
Nutanix Support & Insights
NEW QUESTION # 38
An administrator planned to create a new NC2 cluster and chose the existing AWS VPC infrastructure in the workflow. The administrator needs two private subnets to complete the configuration.
- A. For Prism Element and Prism Central management
- B. For user VMs and cluster management
- C. For private NAT and Elastic IP management
- D. For DNS and NJP management
Answer: B
Explanation:
When creating a new NC2 cluster using an existing AWS VPC infrastructure, two private subnets are needed. These subnets are used as follows:
One private subnet for user VMs, which houses the virtual machines that users interact with.
Another private subnet for cluster management, which is used for internal cluster operations and management tasks, ensuring that management traffic is isolated from user traffic for security and performance reasons.
Reference:
Nutanix Support & Insights
Nutanix Cloud Clusters on AWS Administration
NEW QUESTION # 39
An administrator is planning an NC2 deployment and wants to connect to AWS Services privately from the corporate VPC without going through the public internet.
Which connectivity solution should the administrator use?
- A. Gateway Endpoint
- B. Point-to-Site VPN
- C. VTEP Gateways
- D. Site-to-Site VPN
Answer: A
Explanation:
Gateway Endpoint:
A Gateway Endpoint in AWS allows you to connect to supported AWS services privately without going through the public internet. This setup provides secure and efficient connectivity directly from the corporate VPC to the required AWS services.
Gateway Endpoints support services such as Amazon S3 and DynamoDB and are ideal for scenarios where private connectivity to these services is needed.
Reference:
Refer to the AWS documentation on VPC endpoints, specifically Gateway Endpoints, and the Nutanix documentation on configuring private connectivity for NC2 deployments.
NEW QUESTION # 40
Which two options are prerequisites for deploying an NC2 on AWS cluster? (Choose two.)
- A. A valid CIDR range
- B. A my.nutanix.com account
- C. AWS Direct Connect
- D. An on-premises Prism Central environment
Answer: A,B
Explanation:
A valid CIDR range: A CIDR (Classless Inter-Domain Routing) range is necessary for creating the subnets within the VPC. This range defines the IP address space for the cluster and its components.
A my.nutanix.com account: This account is required to access Nutanix services, including the NC2 console, manage licenses, and perform other administrative tasks.
AWS Direct Connect and an on-premises Prism Central environment are not prerequisites for deploying an NC2 on AWS cluster. While Direct Connect can be used for enhanced network performance and connectivity, it is not a requirement for deployment. Similarly, having an on-premises Prism Central environment is not mandatory for NC2 deployment on AWS.
Reference:
Refer to the Nutanix documentation on NC2 prerequisites and setup guides, and AWS documentation on VPC and subnet creation.
NEW QUESTION # 41
An administrator needs to understand which of the services implemented on their NC2 AWS deployment will be protected with Cluster protect.
Which service of feature is Cluster Protect able to both protect and recover its associated metadata?
- A. VM templates
- B. Files
- C. Categories
- D. Object
Answer: A,B
Explanation:
Cluster Protect in an NC2 environment can protect and recover the following services and their associated metadata:
VM Templates: Ensures that templates used for creating virtual machines are backed up and recoverable.
Files: Protects data stored in Nutanix Files, ensuring that file services are backed up and can be restored as needed.
Reference:
Nutanix Support & Insights
Nutanix Cloud Clusters on AWS Administration
NEW QUESTION # 42
An administrator is deploying a new NC2 cluster on AWS and needs to ensure full connectivity is established between the company's on-premises datacenter and the AWS cloud.
Which two AWS offering will satisfy this requirement? (Choose two.)
- A. ExpressRoute
- B. Direct Connect
- C. AWS VPN
- D. Dedicated interconnect
Answer: B,C
Explanation:
To establish full connectivity between the company's on-premises datacenter and the AWS cloud, the following AWS offerings will satisfy this requirement:
AWS VPN: This service allows you to create a secure connection between your on-premises network or other remote network and your AWS VPC using an IPsec VPN tunnel. It is suitable for low to moderate bandwidth requirements and provides secure, encrypted connections.
Direct Connect: AWS Direct Connect is a dedicated network connection from your premises to AWS. It provides a private, high-bandwidth, low-latency connection which is ideal for high-throughput applications and workloads that need consistent network performance.
Reference:
AWS VPN Documentation
AWS Direct Connect Documentation
NEW QUESTION # 43
Exhibit.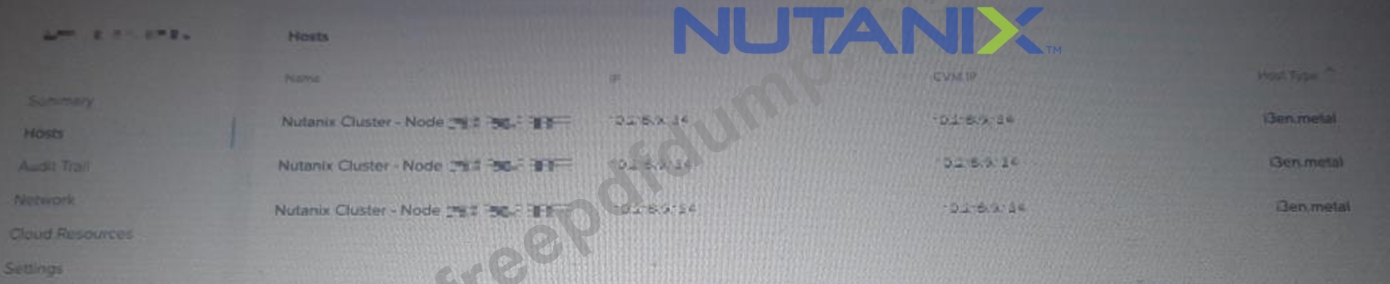
What action is taken against the Condemned node shown in the exhibit?
- A. The node has a power reset sent to it.
- B. The node is powered off.
- C. The node Is automatically replaced.
- D. The node is restarted.
Answer: A
Explanation:
When a node is marked as "Condemned," it indicates that the system has determined that the node is no longer reliable for operations. As part of the automated recovery and protection process, the following action is typically taken:
The node has a power reset sent to it (Answer A):
In most cases, a condemned node undergoes a power reset as an initial recovery attempt. This action attempts to reboot the node to bring it back to a healthy state. If the reset fails, further manual or automated steps may be required to address the hardware or software issue.
Reference:
Nutanix Cluster Management Documentation
Nutanix Support Knowledge Base
NEW QUESTION # 44
Which interface must be used to deploy NC2?
- A. Cloud Provider portal
- B. NC2 Tile within the my.nutanix.com portal
- C. Prism Central Dashboard
- D. Foundation running in a Cloud Virtual Machine
Answer: B
Explanation:
The NC2 Tile within the my.nutanix.com portal is the correct interface to deploy NC2. This portal provides an integrated and user-friendly interface specifically designed for deploying and managing Nutanix Clusters on AWS.
NC2 Deployment Interface:
NC2 Tile within the my.nutanix.com portal: This portal provides the necessary tools and options to deploy and manage NC2 clusters. It includes functionalities for setting up the clusters, configuring network settings, and managing resources.
Advantages:
User-Friendly Interface: Simplifies the deployment process with a guided setup.
Integrated Tools: Provides access to all necessary tools for managing the deployment and monitoring of NC2 clusters.
Reference:
Nutanix Cloud Clusters on AWS Administration Guide
Nutanix my.nutanix.com Portal Documentation
Nutanix Best Practices for Cluster Deployment
NEW QUESTION # 45
Which statement is true regarding AWS account requirements?
- A. AWSCloudFormationFullAccess role is required to create a CloudFormation stack.
- B. NC2 on AWS uses AWS Secrets Manager for maintaining any stored secrets.
- C. IAMFullAccess permission gets configuration details for supported AWS resources.
- D. An AWS root user can be used for any deployment or operations related to NC2.
Answer: A
Explanation:
To create a CloudFormation stack, the AWSCloudFormationFullAccess role is required.
This role grants the necessary permissions to create, update, and delete CloudFormation stacks, which are essential for deploying and managing AWS infrastructure using CloudFormation templates.
CloudFormation stacks are often used to automate the deployment of complex infrastructures, including those required for NC2 on AWS.
Proper permissions ensure that the deployment process is seamless and adheres to the security and operational policies of the organization.
Reference:
Refer to the AWS IAM documentation for details on the AWSCloudFormationFullAccess role and Nutanix documentation on prerequisites for deploying NC2 on AWS.
NEW QUESTION # 46
An administrator is seeking help with an ongoing NC2 issue. After reaching out to Nutanix support, the administrator is introduced to NC2 specialist who can help troubleshoot the problem.
- A. Provide the specialist with the administrator's login credentials.
- B. Ensure the specialist is assigned the RBAC role with proper permissions.
- C. Add the specialist as an admin user to the organizations.
- D. Confirm the Support Authorization on the organization is set to Full Access.
Answer: B,D
Explanation:
Ensure the specialist is assigned the RBAC role with proper permissions (Answer A):
Role-Based Access Control (RBAC) ensures that the specialist has the necessary permissions to troubleshoot and manage the NC2 environment. This avoids unnecessary privilege escalations and maintains security.
Confirm the Support Authorization on the organization is set to Full Access (Answer C):
Setting the Support Authorization to Full Access allows the Nutanix support specialist to have the required access to investigate and resolve issues in the environment. This is essential for effective troubleshooting.
Reference:
Nutanix RBAC Documentation
Nutanix Support Access Guide
NEW QUESTION # 47
Which two features or services can an administrator ensure are protected by cluster protect within an NC2 environment? (Choose two.)
- A. VM Templates
- B. Virtual Machine Disks
- C. Nutanix Files
- D. Flow Network Security
Answer: B,C
Explanation:
Within an NC2 environment, the Cluster Protect feature can ensure the protection of:
Nutanix Files: This provides file services within the Nutanix ecosystem, and Cluster Protect can safeguard the data stored in Nutanix Files.
Virtual Machine Disks: This ensures that the data stored on virtual machine disks is protected, providing backup and recovery options for the virtual machines running within the cluster.
Reference:
Nutanix Cloud Clusters on AWS Administration
Nutanix AOS 6.7 Documentation
NEW QUESTION # 48
If an administrator deploys an NC2 cluster using an existing AWS network, in which type of subnet should the administrator deploy the NAT Gateway?
- A. Isolated subnet
- B. Private subnet
- C. VPN-only subnet
- D. Public subnet
Answer: D
Explanation:
To deploy an NC2 cluster using an existing AWS network, the NAT Gateway should be placed in a public subnet. A public subnet is one that has a route to an Internet Gateway, allowing the NAT Gateway to provide outbound internet access for resources in private subnets. The NAT Gateway is used to enable instances in private subnets to access the internet while keeping them secure by not exposing them directly to the public internet.
Reference:
Nutanix Cloud Clusters (NC2) on AWS Documentation
NEW QUESTION # 49
What is an available log module when configuring a syslog server in the Prism Central Admin Center?
- A. Acropolis
- B. Prism
- C. Zookeeper
- D. API Audit
Answer: A
Explanation:
When configuring a syslog server in the Prism Central Admin Center for Nutanix, one of the available log modules is Acropolis.
The Acropolis module logs system events related to the Nutanix Acropolis operating system, which is critical for monitoring and auditing system activities and performance.
Configuring syslog with the Acropolis module ensures that important events and issues related to the Acropolis environment are captured and can be forwarded to an external syslog server for centralized logging and analysis.
Reference:
Refer to the Nutanix documentation on Prism Central and syslog configuration for the full list of available log modules and detailed steps for configuration.
NEW QUESTION # 50
To manually create an AWS VPC with Public access to Prism Element for testing purposes, Which components must be created?
- A. VPC Subnets Route subnets, Route Tables, NAT Gateway, Internet Gateway, VPN
- B. VPC, Delegated Subnets, Route Tables, NAT Gateway, vNets, Load balancer
- C. VPC, Delegated Subnets, Route Tables, NAT Gateway, Internet Gateway, Load balancer
- D. VPC Subnets Route Tables NAT Gateway, Internet Gateway, Load balancer
Answer: C
Explanation:
To manually create an AWS VPC with Public access to Prism Element for testing purposes, the following components must be created:
VPC: A Virtual Private Cloud to provide an isolated network for the resources.
Delegated Subnets: Subnets within the VPC to segment the network and allocate IP ranges.
Route Tables: To define routing rules for the subnets to ensure proper traffic flow.
NAT Gateway: To enable instances in the private subnets to access the internet.
Internet Gateway: To allow direct internet access to instances in the public subnets.
Load Balancer: To distribute traffic across multiple instances for improved availability and redundancy.
Reference:
Refer to the AWS documentation on VPC creation and Nutanix documentation on network setup for Prism Element access.
NEW QUESTION # 51
An administrator has been tasked with deploying an NC2 cluster on AWS with the requirement to protect workloads. Which two options are valid to protect the workloads on this cluster? (Choose two.)
- A. Use an existing on-prem Nutanix cluster as a disaster recovery target.
- B. Deploy one-node cluster in another availability zone.
- C. Deploy a cluster across two availability zones.
- D. Create a second NCZ cluster in a different availability zone.
Answer: D
Explanation:
To protect workloads on an NC2 cluster on AWS, deploying strategies that ensure high availability and disaster recovery are essential. The two valid options are:
Create a Second NC2 Cluster in a Different Availability Zone:
High Availability: Deploying a second NC2 cluster in a different availability zone ensures that workloads can be quickly recovered in case of an availability zone failure.
Disaster Recovery: This setup enables asynchronous replication between clusters, providing a robust disaster recovery solution.
Use an Existing On-Prem Nutanix Cluster as a Disaster Recovery Target:
Hybrid DR: Leveraging an existing on-premises Nutanix cluster for disaster recovery provides a cost-effective and efficient DR solution.
Replication: Set up replication policies to ensure data is consistently copied from the NC2 cluster on AWS to the on-premises cluster.
Why Not Other Options:
One-node cluster in another availability zone: Not a valid DR solution as a single-node cluster cannot provide the required resilience and high availability.
Deploy a cluster across two availability zones: While this can enhance availability, it is not a typical approach for Nutanix clusters which are designed to operate within a single availability zone for simplicity and performance reasons.
Reference:
Nutanix Cloud Clusters on AWS Administration Guide
Nutanix Disaster Recovery Best Practices
AWS Availability Zones and Disaster Recovery Documentation
NEW QUESTION # 52
......
NCP-CI-AWS Dumps PDF - 100% Passing Guarantee: https://www.freepdfdump.top/NCP-CI-AWS-valid-torrent.html
Latest NCP-CI-AWS PDF Dumps & Real Tests Free Updated Today: https://drive.google.com/open?id=1dEHGRmcUIPh5oMFyyaUNo_X1DyWFqfqd
