

Reliable Windows Server AZ-800 Dumps PDF Jun 24, 2026 Recently Updated Questions
Pass Your Microsoft AZ-800 Exam with Correct 262 Questions and Answers
NEW QUESTION # 103
You have an Azure subscription that contains the following resources:
* An Azure Log Analytics workspace
* An Azure Automation account
* Azure Arc.
You have an on-premises server named Server1 that is onboaraed to Azure Arc
You need to manage Microsoft updates on Server! by using Azure Arc
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point
- A. On Server1, install the Azure Monitor agent
- B. Add Microsoft Sentinel to the Log Analytics workspace
- C. From the Virtual machines data source of the Log Analytics workspace, connect Server1.
- D. From the Automation account, enable Update Management for Server1.
Answer: A,D
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/cloud-adoption-framework/manage/hybrid/server/best-practices/arc-update-management
NEW QUESTION # 104
You are planning the implementation Azure Arc to support the planned changes. You need to configure the environment to support configuration management policies. What should you do?
- A. Deploy the Azure Connected Machine agent to all the servers.
- B. Hybrid Azure AD join all the servers.
- C. Deploy the Azure Monitor agent to all the servers.
- D. Create a hybrid runbook worker m Azure Automation.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/azure-arc/servers/plan-at-scale-deployment
NEW QUESTION # 105
You need to meet the technical requirements for User1. The solution must use the principle of least privilege.
What should you do?
- A. Create a delegation on OU3.
- B. Add Users1 to the Server Operators group in contoso.com.
- C. Create a delegation on contoso.com.
- D. Add Users1 to the Account Operators group in contoso.com.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/identity/ad-ds/plan/delegating-administration-of-account-ous-and-resource-ous
Topic 2, Fabrikam inc.
On-premises Servers
The on-premises network contains servers that run Windows Server as shown in the following table.
DC1 hosts all the operation master roles.
WEB1 and WEB2 run an Internet Information Services (IIS) web app named Webapp1.
On-premises Network
The New York and Seattle offices are connected by using redundant WAN links.
The client computers in each office get IP addresses from their local DHCP server.
DHCP! contains a scope named Scope1 that has addresses for the New York office. DHCP2 contains a scope named Scope2 that has addresses for the Seattle office.
Group Policy Object (GPOs)
The cwp.fabrikam.com domain contains the organizational units (OUs) and custom Group Policy Objects (GPOs) shown in the following table.
Requirements:
Fabrikam Identifies the following planned changes:
* Create a single Azure subscription named Sub1 that will contain a single Azure virtual network named Vnet1.
* Replace the WAN links between the Seattle and New York offices by using Azure Virtual WAN and ExpressRoute. Both on-premises offices will be connected to Vnet1 by using ExpressRoute.
* Create three Azure file shares named newyorkfiles, seattfefiles, and companyfiles.
* Create a domain controller named dc3.corp.fabrikam,com in Vnet1.
* Deploy an Azure Virtual Desktop host pool lo Vnet1. The Azure Virtual Desktop session hosts will be hybrid Azure AD joined.
* License all servers for Microsoft Defender for servers.
* Use Azure Policy to enforce configuration management policies on the servers in Azure and on-premises.
Networking Requirements
Fabrikam identifies the following security requirements:
* Apply GP04 to the Azure Virtual Desktop session hosts. Ensure that Azure Virtual Desktop user sessions lock after being idle for 10 minutes. Users must be able to control the lockout lime manually from their client computer.
* Ensure that server administrators request approval before they can establish a Remote Desktop connection to an Azure virtual machine. If the request is approved, the connection must be established within two hours.
* Prevent user passwords from containing all or part of words that are based on the company name, such as Fab. fabrikam or fsbr! |.
* Ensure that all instances of Webapp1 use the same service account. The password of the service account must change automatically every 30 days.
* Prevent domain controllers from directly contacting hosts on the internet.
File Sharing Requirements
You need to configure the synchronization of Azure files to meet the following requirements:
* Ensure that seattlefiles syncs to FS2.
* Ensure that newyorkfiles syncs to FS1.
* Ensure that companyfiles syncs to both FS1 and FS2.
NEW QUESTION # 106
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains a server named Server1 that has the DFS Namespaces role service installed. Server! hosts a domain-based Distributed File System (DFS) Namespace named Files.
The domain contains a tile server named Server2. Seiver2 contains a shared folder named Share1. Share1 contains a subfolder named Folder 1.
In the Files namespace, you create a folder named Folder! that has a target of \\Server2.contoso.com\Share1\Folder1.
You need to configure a logon script that will map drive letter M to Folder1. The solution must use the path of the DFS Namespace.
How should you complete the command to map the drive letter? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 107
You have an Active Directory Domain Services (AD DS) domain. The domain contains three servers named Server1, Server2, and Server3 that run Windows Server.
You sign in to Server1 by using a domain account and start a remote PowerShell session to Server2. From the remote PowerShell session, you attempt to access a resource on Server3, but access to the resource is denied.
You need to ensure that your credentials are passed from Server1 to Server3. The solution must minimize administrative effort.
What should you do?
- A. Configure Kerberos constrained delegation.
- B. Disable the Enforce user logon restrictions policy setting for the domain.
- C. Configure Just Enough Administration (JEA).
- D. Configure selective authentication for the domain.
Answer: A
Explanation:
Configuring Kerberos constrained delegation allows you to pass your credentials from Server1 to Server3 when accessing a resource. Constrained delegation is a Kerberos feature that restricts the servers to which a service can delegate a user's credentials. This ensures that the delegation is secure and limited to specific services.
NEW QUESTION # 108
You have recently joined the company. Nica and you will be responsible for managing Active Directory Domain Services (AD DS) in the administrator role. You need to set the FSMO role such that the Active directory objects will be unique in every domain. Which of the following Flexible Single Master Operation (FSMO) roles is responsible for the uniqueness of Active directory objects in every domain?
- A. PDC Emulator Role
- B. Infrastructure Master Role
- C. Schema Master Role
- D. RID Master Role
- E. Domain Naming Master Role
Answer: D
Explanation:
When a Domain controller creates a security principal object like a group or a user, it attaches a unique SID (Security ID) to the object. The SID contains:
A domain SID, which is the same for all Security IDs created in a domain.
A RID (Relative ID), that is unique for every security principal Security ID created in a domain.
Reference:
https://docs.microsoft.com/en-us/troubleshoot/windows-server/identity/fsmo-roles
NEW QUESTION # 109
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains two servers named Server1 and Server2.
Server1 contains a disk named Disk2. Disk2 contains a folder named UserData. UserData is shared to the Domain Users group. Disk2 is configured for deduplication. Server1 is protected by using Azure Backup.
Server1 fails.
You connect Disk2 to Server2.
You need to ensure that you can access all the files on Disk2 as quickly as possible.
What should you do?
- A. Create a storage pool.
- B. Install the Data Deduplication server role.
- C. Install the File Server Resource Manager server role.
- D. Restore files from Azure Backup.
Answer: B
Explanation:
Portability: A volume that is under deduplication control is an atomic unit. You can back up the volume and restore it to another server. You can rip it out of one Windows 2012 server and move it to another. Everything that is required to access your data is located on the drive. All of the deduplication settings are maintained on the volume and will be picked up by the deduplication filter when the volume is mounted. The only thing that is not retained on the volume are the schedule settings that are part of the task-scheduler engine. If you move the volume to a server that is not running the Data Deduplication feature, you will only be able to access the files that have not been deduplicated.
https://techcommunity.microsoft.com/t5/storage-at-microsoft/introduction-to-data-deduplication-in- windows-server-2012/ba-p/424257
NEW QUESTION # 110
SIMULATION
You need to create a user named Admin1 in contoso.com. Admin1 must be able to back up and restore files on SRV1. The solution must use principle of the least privilege.
To complete this task, sign in the required computer or computers.
Answer:
Explanation:
NEW QUESTION # 111
You have a server named Server1 that runs Windows Server, has the File Server Resource Manager role service installed, and contains the volumes shown in the following table.
You plan to configure file screens on Server1.
On which volumes can you configure a file screen?
- A. C, E and F only
- B. C and F only
- C. E and F only
- D. C, D, E, and F
- E. F only
Answer: B
Explanation:
File Server Resource Manager (FSRM) in Windows Server can only be configured on volumes formatted with the NTFS file system. It does not support volumes formatted with ReFS or other file systems like ExFAT.
Reference:
https://learn.microsoft.com/en-us/windows-server/storage/fsrm/fsrm-overview
NEW QUESTION # 112
You have a server named Server1 that runs Windows Server. Server1 has the storage pools shown in the following table.
You plan to create a virtual disk named VDisk1 that will use storage tiers. Which pools can you use to create VDisk1?
- A. Pool1 and Pool2 only
- B. Pool2 and Pool3 only
- C. Pool1 and Pool3 only
- D. Pool3 only
- E. Pool only
- F. Pool 2only
- G. Pool, Pool2, and Pool3
Answer: B
Explanation:
In the Administering Windows Server Hybrid Core Infrastructure (AZ-800) study domain for Storage Spaces, Microsoft specifies that storage tiers are created within a single storage pool that contains two classes of media: a fast tier (typically SSD) and a standard/capacity tier (HDD). The guide states that storage tiers "use SSDs for frequently accessed ('hot') data and HDDs for less frequently accessed ('cold') data within the same storage pool," and that tiering is available only when the pool includes both SSD and HDD devices. It further clarifies that different HDD spindle speeds (e.g., 7,200 vs 10,000 RPM) do not constitute different media types for tiering-they are all HDDs.
Applying these rules to the table:
* Pool1 contains only HDDs (7,200-RPM and 10,000-RPM) and no SSDs, so it cannot host a tiered virtual disk.
* Pool2 contains HDDs (10,000-RPM) and SSDs, satisfying the requirement for both media types; it can create a tiered virtual disk.
* Pool3 contains HDDs (7,200-RPM) and SSDs, also satisfying the requirement; it can create a tiered virtual disk.
Therefore, only Pool2 and Pool3 support creating VDisk1 with storage tiers, making option A correct.
NEW QUESTION # 113
You have an on-premises server named Server1 that runs Windows Server and has internet connectivity.
You have an Azure subscription.
You need to monitor Server1 by using Azure Monitor.
Which resources should you create in the subscription, and what should you install on Server1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: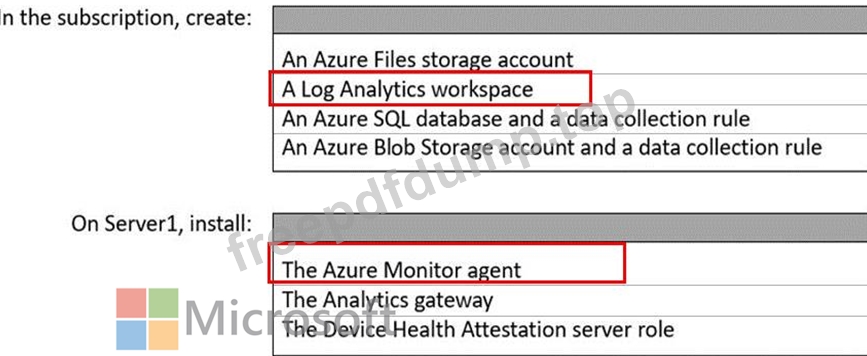
Reference:
https://docs.microsoft.com/en-us/windows-server/manage/windows-admin-center/azure/azure-monitor
NEW QUESTION # 114
Your network contains an on -premises Active Directory Domain Services (AD DS) domain named contoso.
com The domain contains the objects shown in the following table.
You plan to sync contoso.com with an Azure Active Directory (Azure AD) tenant by using Azure AD Connect You need to ensure that all the objects can be used in Conditional Access policies What should you do?
- A. Select the Configure Hybrid Azure AD join option.
- B. Clear the Configure device writeback option.
- C. Change the scope of Group2 to Universal
- D. Change the scope o' Group1 and Group2 to Global
Answer: A
Explanation:
Hybrid Azure AD join needs to be configured to enable Computer1 to be used in Conditional Access Policies.
Synchronized users, universal groups and domain local groups can be used in Conditional Access Policies.
NEW QUESTION # 115
You need to meet the technical requirements for VM1.
Which cmdlet should you run first? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 116
You need to meet the technical requirements for the site links. Which users can perform the required tasks?
- A. Admin1, Adrrun2. and Admin3
- B. Admin1 only
- C. Admin1 and Admin3 only
- D. Admin3 only
- E. Admin1 and Admin2 only
Answer: E
Explanation:
Explanation
Membership in the Enterprise Admins group or the Domain Admins group in the forest root domain is required.
NEW QUESTION # 117
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result these questions will not appear in the review screen.
You have a server named Server1 that runs Windows Server 2022 and has the DHCP Server role. Server1 contains a single DHCP scope named Scope1.
You deploy five printers to the network.
You need to ensure that the printers are always assigned the same IP address.
Solution: You configure the DHCP scope options for Scope1.
Does this meet the requirement?
- A. No
- B. Yes
Answer: A
Explanation:
Correct:
* You create a DHCP reservation for each printer.
Incorrect:
* You create a DHCP address exclusion for each printer.
* You configure the DHCP scope options for Scope1.
* You deploy a DHCP relay agent to the network.
Note:
To configure a specific MAC address to receive an IP address from a particular DHCP scope, you would need to implement DHCP reservations. DHCP reservations allow you to assign a specific IP address to a device based on its MAC address.
Reference:
https://learn.microsoft.com/en-us/answers/questions/1293465/assign-an-ip-to-a-computer-from-a- specific-and-sin
NEW QUESTION # 118
You need to meet the security requirements for passwords.
Where should you configure the components for Azure AD Password Protection? lo answer, drag the appropriate components to the correct locations. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-password-ban-bad-on-premises
NEW QUESTION # 119
......
Latest 2026 Realistic Verified AZ-800 Dumps: https://www.freepdfdump.top/AZ-800-valid-torrent.html
Pass AZ-800 Exam Updated 262 Questions: https://drive.google.com/open?id=1izo_171MGnlStpVuwYNPE1Jcxj-JNp3F
